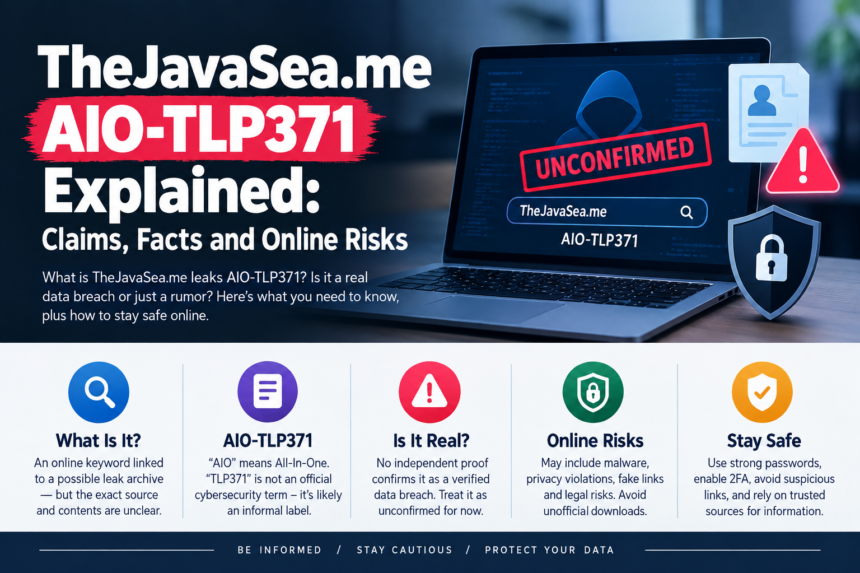
The phrase “TheJavaSea.me AIO-TLP371” has attracted attention across search results, forums, and websites discussing alleged leaked archives. However, the available online descriptions are inconsistent, and the label itself does not establish that a confirmed cybersecurity breach occurred.
Some pages describe AIO-TLP371 as an archive or collection associated with TheJavaSea.me, while other discussions use broader language such as “leak.” Importantly, repeated claims across blogs do not independently verify the origin, authenticity, contents, or legality of the material.
This distinction is especially important when a leak-related keyword may involve private or intimate media. Readers should avoid downloading, redistributing, or attempting to verify questionable archives themselves. Instead, they should rely on trustworthy information and focus on practical privacy and cybersecurity precautions.
What Is TheJavaSea.me AIO-TLP371?
TheJavaSea.me AIO-TLP371 appears to be an informal label associated with an online archive or collection mentioned in publicly indexed discussions.
The term can be divided into three parts:
- TheJavaSea.me — the website name associated with the discussions.
- AIO — commonly used online to mean “All-In-One,” generally describing a bundled collection.
- TLP371 — an identifier that appears to distinguish a particular archive, release, or package.
There is no reliable evidence establishing that “AIO-TLP371” is an official cybersecurity incident name. It should therefore not automatically be interpreted as the name of a database breach, corporate hack, or credential dump.
The label may identify a particular online collection, but the name alone cannot establish where the material originated or whether the material is authentic.
What Does AIO-TLP371 Mean?
Understanding the terminology can help prevent confusion.
AIO
AIO commonly stands for “All-In-One.” Internet communities use the abbreviation for many different types of collections, bundles, and packages.
However, AIO does not mean that a collection is complete, genuine, verified, or officially documented. It is simply a descriptive label that may have been chosen by the person or community responsible for naming an archive.
TLP371
The TLP portion can be confusing because cybersecurity professionals use TLP to mean Traffic Light Protocol, a legitimate framework for communicating how sensitive information should be shared.
The official framework uses designations such as TLP:RED, TLP:AMBER, TLP:GREEN, and TLP:CLEAR.
TLP371 is not an official Traffic Light Protocol classification.
Therefore, in the context of AIO-TLP371, the term appears more likely to be an informal archive identifier than a recognized cybersecurity designation.
The number 371 could represent a batch, release, sequence, or internal naming convention. There is not enough reliable public documentation to establish exactly what the number represents.
Is AIO-TLP371 a Confirmed Data Breach?
This is one of the most important distinctions surrounding the topic.
The available information does not establish AIO-TLP371 as a confirmed conventional cybersecurity data breach.
A genuine breach investigation would normally involve evidence such as:
- An official statement from an affected organization
- Analysis from identifiable cybersecurity researchers
- Technical information about the incident
- Evidence concerning the affected systems
- A documented incident timeline
- Information about what categories of data were exposed
An archive label or forum post does not provide the same level of verification.
Some online pages may describe AIO-TLP371 as a “leak,” but the word leak can be used very broadly online. It can refer to anything from an alleged private-media collection to stolen files, credentials, documents, or other material.
Consequently, readers should distinguish between “an online claim exists” and “a security incident has been independently confirmed.”
Why Are There So Many Different Claims?
Leak-related topics can spread rapidly because websites often publish articles based on information already appearing elsewhere.
This creates a potential repetition effect.
For example, one page might publish an unsupported description of an archive. Another website may summarize that page. A third website may use the second article as its source. After several repetitions, the original claim can appear to have widespread confirmation even though no independent investigation has taken place.
This is particularly relevant to unusual identifiers such as AIO-TLP371.
A technical-looking name can make an online claim appear authoritative. But terminology alone is not evidence.
When evaluating a leak report, ask:
- Who originally reported it?
- Is there independent evidence?
- Has an affected organization acknowledged the incident?
- Have reputable security researchers analyzed the material?
- Are specific technical details available?
- Do independent sources agree on the basic facts?
If the answer to most of these questions is no, the claim should remain classified as unverified.
What Kind of Material Is Associated With the Keyword?
Public discussions have used different descriptions for AIO-TLP371. Some references characterize it as an archive involving adult media, while others use generic terms such as “leaked content” or “data collection.”
Because these descriptions are not independently established, it would be misleading to present any particular list of contents as confirmed fact.
More importantly, if an archive contains intimate or personal material, its existence does not establish:
- Who created the material
- Who owns it
- Whether the people depicted consented to distribution
- Whether the material was obtained lawfully
- Whether every person depicted was an adult
- Whether the files are authentic
- Whether the files have been altered
- Whether downloading them is safe
These uncertainties are significant enough that users should not attempt to obtain the archive simply to investigate the claims themselves.
Privacy Risks Connected With Alleged Leak Archives
Even when the underlying story is uncertain, leak-related archives can create serious privacy concerns.
If private images or other personal information are distributed without permission, further copying can increase the harm to the people involved.
An archive being publicly indexed does not mean that everyone shown in it agreed to publication.
This is particularly important with intimate material. Users should avoid reposting images, identifying people, sharing download links, or attempting to determine someone’s identity from alleged leaked content.
A responsible approach is to focus on consent, privacy, and legitimate reporting mechanisms, rather than treating alleged leaked material as entertainment.
Cybersecurity Risks of Unknown Downloads
There is another important issue: the download itself may be dangerous.
Websites promoting alleged leak archives may use suspicious download pages, redirects, advertisements, fake verification screens, or executable files.
Potential risks include:
- Malware
- Credential theft
- Browser notification abuse
- Phishing
- Malicious browser extensions
- Account compromise
- Tracking and privacy invasion
A ZIP, RAR, PDF, video, or other file extension does not guarantee that a download is safe.
For this reason, users should not download AIO-TLP371—or similar unverified archives—to determine whether the claims are genuine.
You do not need to possess questionable files to protect yourself.
What Should You Do If You Encounter the Keyword?
If you encounter a page discussing TheJavaSea.me AIO-TLP371, the safest response is to avoid interacting with questionable downloads.
Instead:
1. Don’t download the archive
Do not download, extract, execute, or redistribute files from an unknown leak source.
2. Don’t enter account credentials
If a page asks you to log in before viewing alleged leaked material, treat the request cautiously. Never reuse your normal password on an unfamiliar website.
3. Don’t share intimate material
If the alleged archive involves private or intimate content, do not forward it, repost it, or send copies to other people.
4. Check trustworthy sources
Look for official statements, established cybersecurity reporting, or independent technical analysis rather than relying exclusively on websites repeating the same claim.
5. Protect your accounts
Using unique passwords and multi-factor authentication provides protection against many common account-compromise scenarios.
What If You Already Visited a Suspicious Page?
Simply opening a webpage does not automatically mean your device has been compromised. However, additional precautions make sense if you downloaded something, installed software, entered credentials, or noticed unusual behavior afterward.
Consider these steps:
Change compromised passwords. If you entered a password on a suspicious website, change it immediately from a trusted device. Do not reuse the replacement password elsewhere.
Enable two-factor authentication. MFA adds another security layer if your password becomes exposed.
Review active sessions. Check your important accounts for unfamiliar devices or login sessions.
Remove suspicious browser permissions. If you accidentally allowed notifications or other permissions, remove them through your browser settings.
Update your software. Install current operating-system, browser, and security updates.
Run a security scan. If you downloaded an unfamiliar file, use reputable security software to scan the device.
Monitor important accounts. Pay attention to unexpected password-reset emails, login alerts, account changes, or other unusual activity.
What If the Material May Depict You?
If you believe private or intimate material involving you has been distributed without permission, do not download additional copies just to collect evidence.
Instead, document the relevant information without redistributing the material. Depending on the circumstances, useful information may include:
- Page URL
- Website or platform name
- Username or account name
- Date and time
- Messages containing threats
- Screenshots of relevant non-explicit information
You can then use the platform’s reporting process or an appropriate legal or victim-support channel.
Search-engine removal and source removal are also different processes. Removing a search result does not necessarily remove the original material from the website hosting it.
How to Evaluate Future Leak Claims
The lessons from AIO-TLP371 can be applied to almost any online leak story.
Before treating a claim as established fact, look for evidence.
Look for independent confirmation
A trustworthy report should ideally have information from sources that did not simply copy one another.
Look for an affected organization
If someone claims that a particular company suffered a breach, check whether the organization has published a security notice or statement.
Look for technical evidence
Serious cybersecurity investigations often contain technical details that can be examined by independent researchers.
Check the dates
Old archive references can be presented as new incidents when they are rediscovered years later. Always check the original publication or indexing date.
Separate claims from evidence
A website saying “the leak contains millions of records” is not the same as independently demonstrating that those records exist.
Be cautious with download-based verification
You should never have to compromise your own device simply to determine whether an internet rumor is true.
AIO-TLP371 vs. a Confirmed Breach
| Issue | What can currently be said |
| AIO-TLP371 name | Appears in online discussions |
| “AIO” meaning | Commonly means “All-In-One” |
| TLP371 | Not an official Traffic Light Protocol label |
| Confirmed database breach | Not established by the supplied public information |
| Archive authenticity | Not independently established |
| Exact contents | Unclear |
| Consent of depicted individuals | Cannot be established from the label |
| Download safety | Cannot be guaranteed |
| Best user response | Avoid downloads and verify information through trustworthy sources |
This distinction is central to understanding the topic. An online archive label is evidence that a label is being used—not automatic evidence that every claim attached to it is true.
Conclusion
TheJavaSea.me AIO-TLP371 is best treated as an unverified online archive-related label rather than automatically calling it a confirmed cybersecurity breach.
The terminology can sound technical, but AIO-TLP371 is not an established cybersecurity classification, and the label itself cannot verify the source, authenticity, contents, consent status, or safety of any associated files.
The most useful response is therefore not to chase alleged leaked material. Avoid suspicious downloads, do not redistribute private content, protect your accounts with strong unique passwords and MFA, and evaluate claims through independent and trustworthy sources.
In cybersecurity and online privacy, verification matters more than repetition. A claim appearing across many websites does not necessarily make it independently confirmed.
FAQs
What is TheJavaSea.me AIO-TLP371?
TheJavaSea.me AIO-TLP371 is an online keyword associated with an alleged archive or collection discussed on the web. The available descriptions do not independently establish its origin, authenticity, or complete contents.
Is AIO-TLP371 an official cybersecurity term?
No. While TLP is associated with the legitimate Traffic Light Protocol, AIO-TLP371 is not an official TLP classification.
Does AIO mean the archive is complete?
No. “AIO” commonly means “All-In-One,” but it does not guarantee completeness, authenticity, or accuracy.
Is AIO-TLP371 a confirmed data breach?
The available information does not independently establish it as a conventional confirmed data breach. Readers should distinguish online claims from verified security reporting.
Should I download AIO-TLP371 to check whether it is real?
No. Downloading an unknown archive can expose your device and accounts to security threats and can create additional privacy and legal concerns, particularly if the material involves private or intimate content.
What should I do if my information may have been exposed?
Use unique passwords, enable multi-factor authentication, review account activity, and follow official notifications from the relevant service. If intimate material involving you has been distributed without consent, use the platform’s reporting and removal mechanisms rather than downloading or redistributing the material.